Showing posts with label Spam Reports. Show all posts

Only 11% of Security Incidents Are Reported -

Although 49% of the companies that took part in a survey conducted by RSA Conference said that their primary security concern was data leakage, such as employee or customer information, and 29% of them were in fact confronted with the problem in 2007, only 11% actually reported the incidents.

"Security professionals need to remain cognizant of the regulations that their organizations must comply with and ensure they are taking steps to properly report the security incidents that are required by law – whatever they may be." said Tim Mather, Chief Security Strategist, RSA Conference. With no reports from the organizations that were affected, it is more and more difficult for both security specialists and legal regulators to take the right measures to reduce online security incidents.

Aside from data theft, companies showed that they are mostly worried about email-borne malware/phishing (41%), web-borne malware, insider threats/theft (both up to 36%), intellectual property theft (34%) and known software vulnerabilities (24%).

Although they seem concerned with the probability of an attack, 46% of the companies that responded to the survey said they didn't face any security incident in 2007. 13% of them were less lucky, reporting over 20 attacks in one single year.

Speaking of those for whom 2007 was not a peaceful year at all, 69% of the companies that indicated they had to deal with security threats last year said that email-borne malware/phishing was the pain in the neck for them. 44% faced web-borne malware, while 16% admitted that not only their data, but their finances also were struck by organized crime for commercial gain. Mobile phone or smartphone malware that tried to affect the computer systems of the companies was reported by only 9% of them, but it doesn't mean that this is a field where Internet offenders have said their final word.

[Source: softpedia]

Text-Based Spam Revival

Spammers radically changed their methods from what they used last year. If, at the end of June 2007, 60% of spammers used images in order to make people swallow the bait, the percentage dropped to 3% at the end of June 2008. On the other hand, after conducting a global study, BitDefender researchers noticed the revival of text spam – 70% of the spamming attacks are now text-based, compared with the 20% that was recorded last year.

"Plain-text continues to be the most prolific medium for e-mail spam istribution, especially due to its simplicity, reduced size and extreme versatility," said Vlad Valceanu, head of BitDefender AntiSpam Research Lab.
The methods used to spread malware in the first six months of 2008 were reported as being, in order, downloaders, malicious advertising, bundle applications, social engineering and information websites, autorun and file infectors, email spam and peer-2-peer networks.

As expected, considering the immense number of emails with a medical subject that are received by almost anyone, the team that works in the anti-virus field said that content related to drugs is the most used, worldwide, to spread malicious software. Replica watches placed second in the top of most popular subjects to be delivered by spammers via email.

Phishing tools were also popular in the first half of 2008. Those who were especially targeted were native English speakers from the US, UK or Canada, who were tempted with counterfeited offers, mainly from US banks and other financial institutions. Most of the messages were alarming, in order to make people react impulsively – they were relating about blocking or expiration of accounts, while also asking for private information that was to be used to enhance security.

"Spammers and phishers continued to improve their skills in replicating and forging legitimate message characteristics. However, the simple text e-mails proved their efficiency as well, rounding up the total figure of ID theft victims to 50,000 each month," added Vlad Valceanu.

[Source: softpedia]

No URLs in Recent Phishing Attempts

According to research conducted by Internet security company TrendMicro, phishers are resorting to new ways of fooling users. The ever present URL to the phishing site has no longer been seen in numerous messages analyzed by TrendMicro. It would seem that instead the user is provided with a legitimate e-mail address.

A run of the mill phishing attempt involves the user receiving a spam message that directs that user to a phishing site. You will receive a message that goes something like "you need to update your bank account info, please click on the following link", but by doing so you will be directed to a web page that looks very similar to the one of your bank. And by filling in the requested information you are only playing into the hands of the phisher.

"But now, there’s no URL seen in new phishing email samples we’ve discovered. They display instead a legitimate email address. This is to trick users that the recipient of the user name and password they will send is a legitimate user, but looking at the source code of the mail, it would go to an individual email address, the phisher’s," says Aivee Cortez from TrendMicro.

One such spam message circulating on the Internet lately was informing users that they needed to upgrade their EarthLink account. As you might have already figured it out, the user is not asked to click on a link and visit a phishing site, but instead is asked to forward the username and password of the account to what seems to be the customer support e-mail address. Just to make sure the phishing attempt is successful, the message informs you that your account will be deleted unless you send out that information.


It even goes as far as to say "this is an Administrative Message from EarthLink. It is not spam. From time to time EarthLink will send you such messages in order to communicate information about your subscription." By simply claiming not to be spam and to originate from the actual site, the message seems authentic. But as a rule of thumb you should never send out security credentials such as username and password, no matter who asks for it. It is one of the basic rules of keeping your data nice and safe.

[Source: softpedia]

New Storm Spam Campaign Exploits NACU Rumors -

TrendMicro, company that specializes in Internet content security, reports that the Storm botnet is once again attempting to propagate its malicious software. The means to do so is by sending out spam messages which inform about a financial crisis that will engulf the world's economy. A link is of course provided and you are invited to click on it, but by doing so you may become infected with the Storm worm, and your computer will end up as just another zombie in the Storm botnet.

TrendMicro detects new Storm spam campaign

According to the spam message, the NACU (North American Currency Union) is secretly planning to bring the currencies of North America, Canada and Mexico together, and come up with a new currency called "amero".

Here is an excerpt from the spam message itself: "You can forget about dollars. The U.S. Government began to realize the plan to replace the Dollar with the "Amero", the new currency of the North American Currency Union. Canada, the United States of America and Mexico have resolved to unit in order to resist the Worldwide Financial Crysis. You can become acquainted with the plan of the implementation of Amero, just click on the icon underneath this text."

Users should be warned that there is no such organization, and there never was. It is all noting but a clever scheme that the spammer has come up with in order to make the message seem believable.

"Neither amero nor the North American Currency Union exists of course, as these remain ideas only, at least for today. Conspiracy theories abound, however; there are rumors about secret pacts between the United States, Canada, and Mexico, but these remain unsubstantiated. Last year, there were reports of the United States Treasury issuing amero coins, but this was later proven to be untrue," says Jake Soriano from TrendMicro.

As a rule of thumb you should not open unsolicited mail, but if you can’t resist the temptation, you should at least not click on any links provided in said mail. Keep in mind that believable, accurate news come from trusted sites and news portals, not from spam messages. Not only will you be misinformed, you will become infected and aid in the expansion of the Storm botnet.

[Source: softpedia]

Chinese Earthquake 419 Scam

The world is still terrified by the earthquake which shook down China on May 12 and scammers, hackers and phishers still want to take advantage of this. Another
scam was detected by security company Sophos under the form of a 419 email which asks readers for their money. The only difference from a traditional 419 scam is that this time, the sender asks for money in order to go to China and look for his wife.

"I do not know your exact name. I can only guess. I ask you to read through my letter up to the end. And still, if you will be able to help me I shall consider you to be the best man in this world. You will save a life of mine Jin. I shall write the data on which I will be able to receive cashes in Philippines through Western Union," a scrap of the email reads.

As you know, several other scams could be seen these days on the web, most of them being somehow related to the Chinese earthquake. If in some cases the hackers attempted to break into the Red Cross servers and steal donations, some other attackers relied on news stories through which they attempted to trick people into downloading a malicious Word document which could compromise their computers.

"Spammers and scammers are always ready to jump on the latest disaster or big news headline to try and exploit users. Past examples of similar scams include the Concorde air disaster, the London bombings, and the war in Iraq," Zoe Markham, SophosLabs UK, explains.

There's not much to do with such emails but to delete them. However, extra-care is recommended these days when more and more scams attempt to take advantage of the Chinese tragedy.

[Source: softpedia]

More Celebrity Pictures Spread by Mail

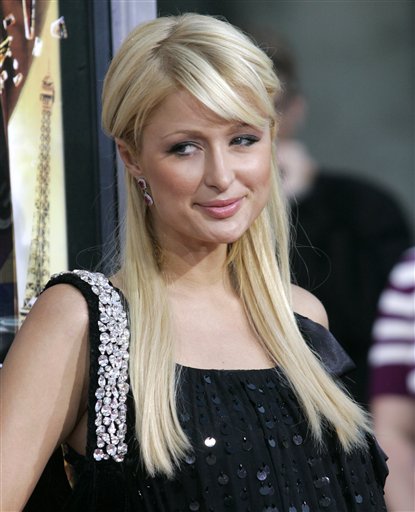
Paris Hilton is, once again, used in spam attacks
Celebrities have always been some of the most popular subjects on the web and spammers know it. That's why an important percentage of their attacks actually rely on
celebrities, lots of messages promising hot pictures with Paris Hilton, Angelina Jolie and many other stars. However, the purpose of these emails is actually to drop malware on readers' computers and steal sensitive data or infect their systems. A similar attack has been detected this weekend by security company Sophos which disclosed more information about the new spam avalanche.

First of all, the subjects vary by email but all messages have the same attachment named xjolie.zip. Most emails have the following subjects: "Something hot", "Hot news", "Paris Hilton" and "Hot pictures", Vanja Svajcer, SophosLabs, UK, explained. Obviously, downloading the attached zip archive attempts to drop a Trojan horse, in our case, Troj/Agent-HAH.

"Unfortunately I have not manged to make the Trojan to run successfully under our controlled environment. Every time launched the file causes an exception so I cannot give you more details about what it would do if it would run successfully," the Sophos official said.

Similar spam attacks occur every once in a while, so keeping your anti-virus up-to-date with the latest virus definitions should be the easiest way to stay on the safe side. However, extra-care is recommended when reading suspicious emails because spammers simply don't want to abandon their attacks and "hot pictures" may reach your inbox on a daily basis.

Unfortunately, there were cases when such attacks could cause even more damage and were especially intended to take advantage of security vulnerabilities spotted in the operating system or in the application installed on computers. That's why updating the programs and the operating system, as well as applying the latest patches for your security products would be a simple and useful method to avoid getting your computer compromised.

Source: softpedia]